

95·
5 days agoWhat the hell is this AI slop?
What the hell is this AI slop?
Crypto Bro -> https://cointelegraph.com/opinion/web3-has-a-metadata-problem , https://bitcoinmagazine.com/technical/why-mixnets-are-needed-to-make-bitcoin-private
Also they love using LLM trained on our works (devs) : https://nym.com/blog/bug-bounty-ai-age
About the fascism I understand that few people here (proportionally) seems to not be educated on the topic (I see to many pedolandians or canadians in here maybe) : fascism is not being a bad guys wanting to control everyone, lots of monarchs were that way, this is not fascism. Fascism is the bourgeoisie (the social class owning the properties, even more so the means of productions) taking power over society, the more power they grab the deeper you’re in fascism. That’s why many western people do not understand they live in fascist societies while they can agree that money is the real power, not the decrepit old white man put in front (thus they don’t understand fascism, and I think this is on purpose, from schools to media).
So a senior research scientist at MIT (CEO) and a founder of Swiss crypto brokerage and financial services firm (COO) decided to create a company in… wait for it… Switzerland! Famous country know for it fight against the aggression of the bourgeoisie for the last century and its strong stance against today’s genocides. Definitely not known for being the Nazi’s gold vault and all sorts of awful money laundering. If you understand that fascism come from the people who owns the money what do you think about private banks? Swiss is fascists’ paradise and it always have been.
I can close my eyes on Swedish people establishing in Sweden, or anyone in his European country, even if the actual government is far-right there or not. But this is not really the case here, it’s more like the Y-combinator guys establishing in Delaware or… Cayman Islands! This is 101 people only seeking money at the expense of everyone else. Hence my point of view this is already quiet deep in fascism, even if there are smart enough not to open their mouth about Palestine and keeping themselves into crypto-broing and “privacy” (I could totally see them loving anarcho-capitalism).
Also bonus : what social media do they choose? OH NO! Linkedin and Twitter, I wouldn’t have guessed. If you want maximum cringe check the avatar -> https://www.linkedin.com/in/alexis-roussel-01993143/
Yet an other swiss based facsist company with a touch of crypto bro. No thanks.
Suggests to join the community on Reddit and no web version.
Maybe it’ll get better over time. I’ll keep the name in mind.
could you be more explicit? not that I do not trust you but I’d like to know more.

it is sad to see people falling again and again on the same traps.
Murena is not our friend, it is very much business-minded, and /e/os is also lacking in privacy and customer respect (going straight to the worse of AI company with OpenAI, pushing/forcing you into their VPN stuff)
Here we have a 1200€ phone (who buys that? Tesla owners?) with 2022 hardware (Mali g615, really?) and amoled screen we never asked for (maybe Linux tech tips kinda folks want that yeah).
I like privacy indeed, give me linux please, don’t sell me half-decade old hardware for insane price just because “hardware kill switch” (librem guys came back?). Don’t shove amoled in my throat and give me my reliable audio jack. Then we’re talking
deleted by creator
What’s nova launcher? All I can find is a seemingly proprietary Android launcher with a Twitter as only social media. Doesn’t scream FOSS to me.
hosted on GitHub, the irony…
it used to be cheaper, and with an audio jack. Add some environment and social consideration and I see many reasons to buy it.
Or you can buy a Google phone from Amazon and text about privacy or freeing Palestine while sipping your Starbucks coffee in your Tesla car.
Not everything has to be about how much do you personally get for the money you give.
I am so glad I could get the Faiphone 3 while it still had an audio jack. At that time the hardware was not too far behind, still too much for my use which is mainly scrolling through obscure left-ish forums and YouTube channels (thanks newpipe) and startups late-stage capitalist hacker news (I don’t know any better about tech).
Are we implying that we should tap every phone call?
We can say a lot of very bad stuff over the phone too. Should we have a way to prevent this?
I had the idea that moderation is instance based in Lemmy, mods only moderate people on their instance.
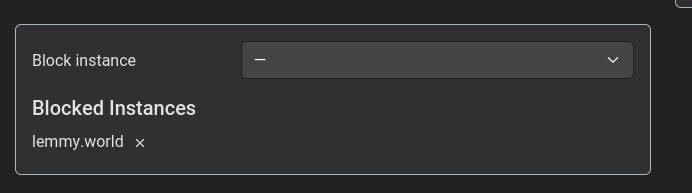
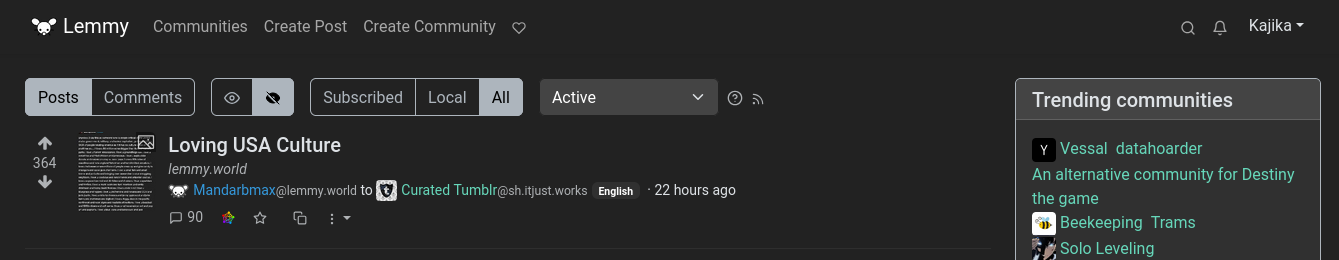
I must be missing something (I can see the community is not from lemmy.world but the guy is)
OK I got it, you are completely out of the loop here.
You do not grasp the idea of NoScript and other JS filtering extension. This is not about server code, your all arguments is baseless here.
By the way JS refered to Javascript and not NodeJS.
Anyway I got you whole company/business talk about “keeping the service available, secure, performant” and “GDPR […] bankrupting fine”… yeah lemmy.world.
Thanks for your answer.
First I don’t even grasp what a “service owner” is.
Second, for JS front-end openness there are already a bunch of app (web, android) that are open-source and secured. Everything has dependencies nowadays, this doesn’t prevent good security. Think all the python app and their dependencies, rust, android… even c\c++ packages are built with dependencies and security updates are necessary (bash had security issues).
I think with JS scripts it’s actually even easier to have good security because the app is ran in our web browser so the only possible attacker is the website we are visiting itself. If they are malicious then the close-sourced JS script is even worse. Unless you count 3rd party scripts embedded that bad dev uses in their website without even thinking about trusting them. That is also awful in both open or close source environment.
So even having imperfect security (which happens regardless to openness), who is the attacker here? I would rather run js script on my end if the code can be checked.
I believe you missed the point, I am not in defense of Security through obscurity (https://en.wikipedia.org/wiki/Security_through_obscurity), quiet the opposite.
The point: “[…] risk for the service owner as it gives an easily parsable way for an attacker to check […]” is well known and not the discussion here. You can choose close source for ‘security’ this is opensource community so I am wondering about such a tool.
There’s no “open source” centralized website. You can’t know what the server is effectively running unless you have access to it. To me this makes no sense.
I tried watching the video. I am genuinely interested but I couldn’t. The video is uncuted (edit: uncut*, my English is so bad) and very slow paced. After 10 minutes I gave up (50 minutes remaining).
Maybe an other time or with an other video.
He is right. In Japan there are 2 form of health insurance: from your company 社会保険 (shakai houken) or directly from the government 国民健康保険 (kokumin kenko houken). If you quit your job you loose your health insurance the very day you’re unemployed and must go to your prefecture to ask the national one (you’ll pay for it, around 200$-300$ a month).
Also in France your health insurance is also tied to your job. The french administration is a nightmare to me so I have no idea how to get anything if you’re unemployed.
Is this even legal to not identify yourself while selling a product?